Code Is Becoming Part of the Deal Structure
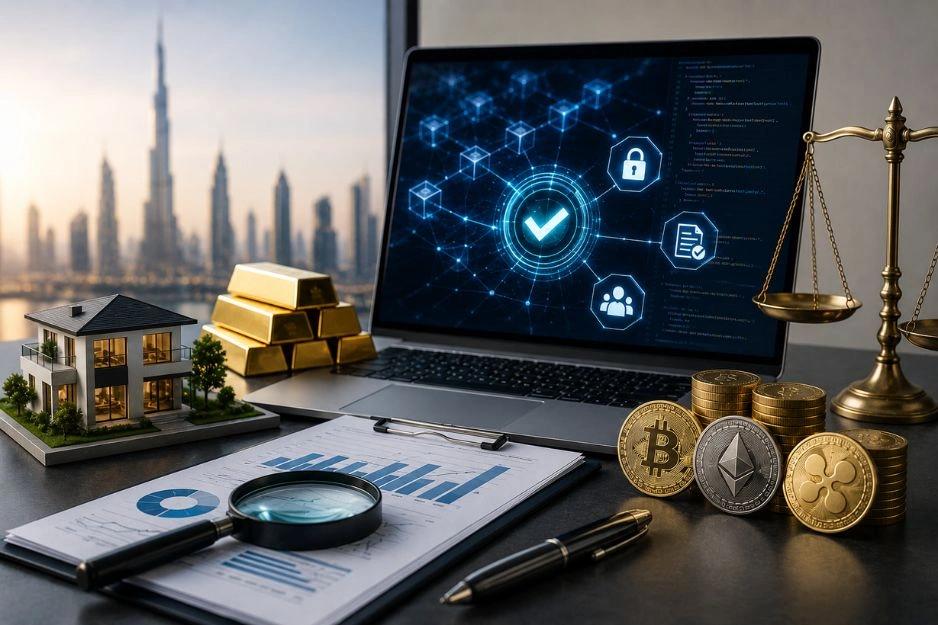
Smart contracts are increasingly moving from technical infrastructure into the commercial layer of high-value transactions. Tokenised real estate, tokenised gold, automated payments, digital investment instruments, and virtual asset settlement models all depend on code that executes business logic once specific conditions are met.
This creates a new compliance challenge. In traditional transactions, firms can review contracts, invoices, payment records, ownership documents, and approval trails. In tokenised transactions, part of the transaction logic may sit inside smart contract code, oracle inputs, wallet permissions, and automated execution rules.
For DNFBPs, this matters because weak technical controls can become weak compliance evidence. If a tokenised transaction fails, routes funds incorrectly, gives excessive access to an administrator, or executes based on unreliable external data, the issue is no longer only technical. It becomes a governance, due diligence, and transaction risk problem.
Smart Contract Assurance Moves Beyond Cybersecurity
A recent AKW Consultants article on smart contract audits highlights how automated execution, oracle dependency, access controls, and code vulnerabilities can affect high-value transactions. This is highly relevant in the UAE, where tokenisation models are increasingly linked to real-world assets, investment structures, and regulated virtual asset activity.
VARA’s Technology and Information Rulebook sets clear expectations for VASPs using smart contracts, including static and dynamic code analysis, independent third-party audits before deployment, formal verification where applicable, penetration testing, and regular reassessment of deployed contracts.
Although VARA obligations apply within the relevant virtual asset regulatory perimeter, the wider message is important for DNFBPs. When clients introduce tokenised assets or crypto-linked transaction flows into real estate, precious metals, legal structuring, or company service activity, compliance teams need stronger evidence that the technology behind the transaction is reliable, traceable, and properly governed.